Before running UFM:
-
Perform Initial Configuration
-
Ensure that all ports used by the UFM server for internal and external communication are open and available. For the list of ports, see Used Ports.
You can run the UFM server software in the following modes:
-
-
Running UFM in High Availability with failover to an external SM
In Management or High Availability mode, ensure that all Subnet Managers in the fabric are disabled before running UFM. Any remaining active Subnet Managers will prevent UFM from running.
Running UFM Server Software in Management Mode
After installing, start the UFM Server by running:
systemctl start ufm-enterprise.service
The /etc/init.d/ufmd script is available for backward compatibility.
Log files are located under /opt/ufm/files/log (the links to log files are in /opt/ufm/log).
Running UFM Software in High Availability Mode
On the master server, start the UFM Server by running:
ufm_ha_cluster start
You can specify additional command options for the ufmha service.
ufm_ha_cluster Command Options
|
Command |
Description |
|---|---|
|
|
Starts UFM HA cluster. |
|
|
Stops UFM HA cluster. |
|
|
Initiates failover (change mastership from local server to remote server). |
|
|
Initiates takeover (change mastership from remote server to local server). |
|
|
Shows current HA cluster status. |
|
|
Cleans the HA configurations on this node. |
|
|
Displays help text. |
HTTP/HTTPS Configuration
By default, UFM is configured to work with the secured HTTPS protocol.
After installation, you can change the Web Server configuration to communicate in a secure (HTTPS) or non-secure (HTTP) protocol.
To change the communication protocol, use the following parameter under the [Server] section in the gv.cfg file:
-
ws_protocol = https
Changes take effect after you restart UFM.
UFM Internal Web Server Configuration
UFM uses Apache as the main web server for external client access. UFM uses an internal web server process, to which Apache forwards the incoming requests.
By default, the internal web server listens to the local host interface (127.0.0.1) on port 8000.
To change the listening local interface or port, use the following parameters under the [Server] section in the gv.cfg file:
-
rest_interface = 127.0.0.1 -
rest_port = 8000
Changes take effect after you restart UFM.
User Authentication
UFM User Authentication is based on standard Apache User Authentication. Each Web Service client application must authenticate against the UFM server to gain access to the system.
The UFM software comes with one predefined user:
-
Username: admin
-
Password: 123456
You can add, delete, or update users via User Management Tab.
UFM Authentication Server
The UFM Authentication Server, a centralized HTTP server, is responsible for managing various authentication methods supported by UFM.
Configurations of the UFM Authentication Server
The UFM Authentication Server is designed to be configurable and is initially turned off by default. This means that existing authentication methods are managed either by the native Apache functionality (such as Basic, Session, and Client Certificate authentication) or at the UFM level (including Token-Based authentication and Proxy Authentication).
Enabling the UFM Authentication Server provides a centralized service that oversees all supported authentication methods within a single service, consolidating them under a unified authentication API.
Apache uses the authentication server's APIs to determine a user's authentication status.
To enable the UFM Authentication Server, see Enabling UFM Authentication Server.
All activities of the UFM Authentication Server are logged in the authentication_service.log file, located at /opt/ufm/files/log.
Azure AD Authentication
Microsoft Azure Authentication is a service provided by Microsoft Azure, the cloud computing platform of Microsoft. It is designed to provide secure access control and authentication for applications and services hosted on Azure.
UFM supports authentication using Azure Active Directory. To set it up, follow the steps in the following sections.
Register UFM in Azure AD Portal
To log in via Azure, UFM must be registered in the Azure portal using the following steps:
-
Log in to Azure Portal, then click Azure Active Directory in the side menu.
-
If you have access to more than one tenant, select your account in the upper right. Set your session to the Azure AD tenant you wish to use.
-
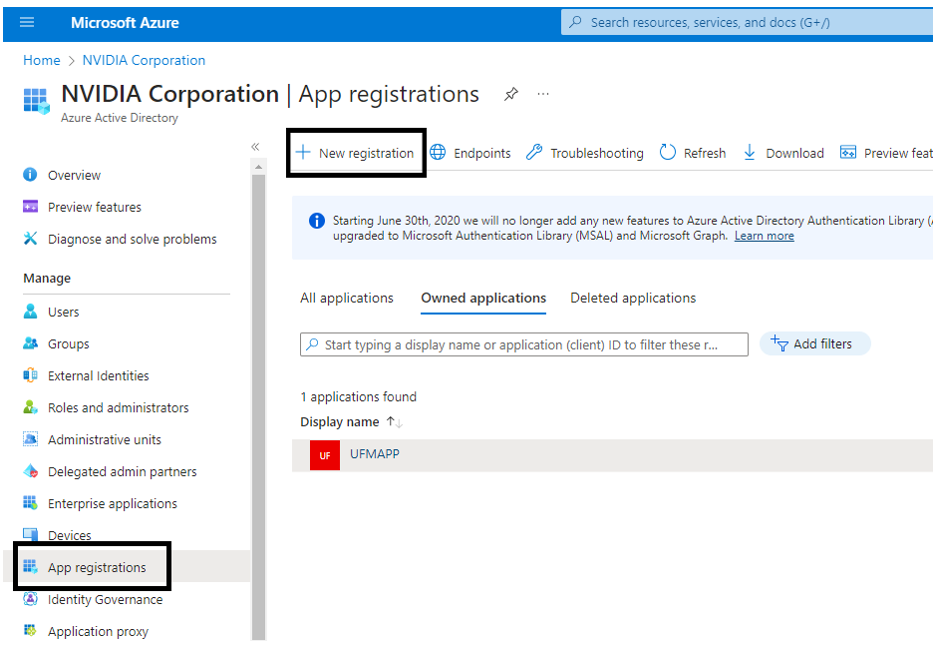
Under Manage in the side menu, click App Registrations > New Registration.
-
Provide the application details:
-
Name: Enter a descriptive name.
-
Supported account types: Account types that are allowed to log in and use the registered application.
-
Redirect URL: Select the app type Web, and add the following redirect URL:
https://<ufm_server>/auth/login
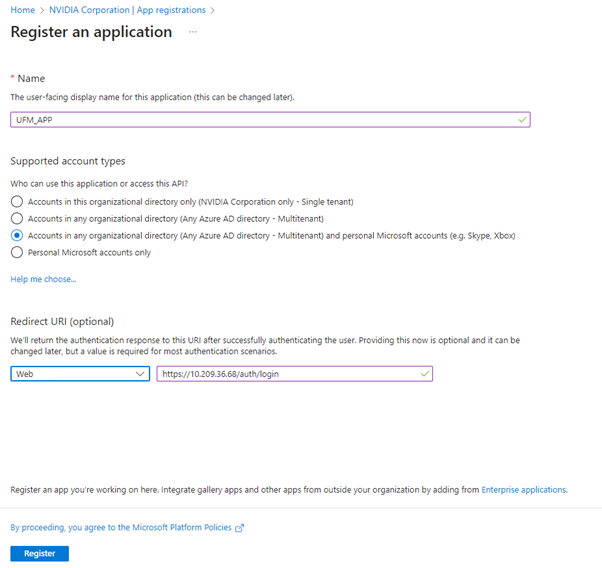
Then, click Register. The app’s Overview page opens.
-
-
Under Manage in the side menu, click Certificates & Secrets > New client secret.
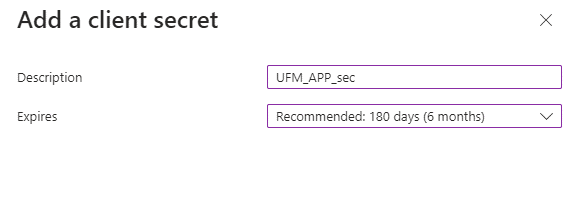
Provide a description for the client secret and set an expiration time, then click Add. -
Copy the client secret key value, which you need to configure UFM with Azure AD. The value of the generated secret is hidden after you leave the page, and you cannot copy or read it.
-
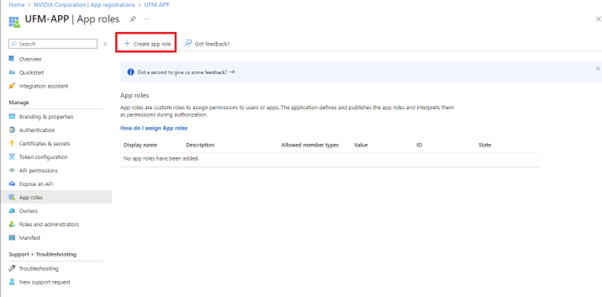
Under Manage in the side menu, click App roles > Create app role.
-
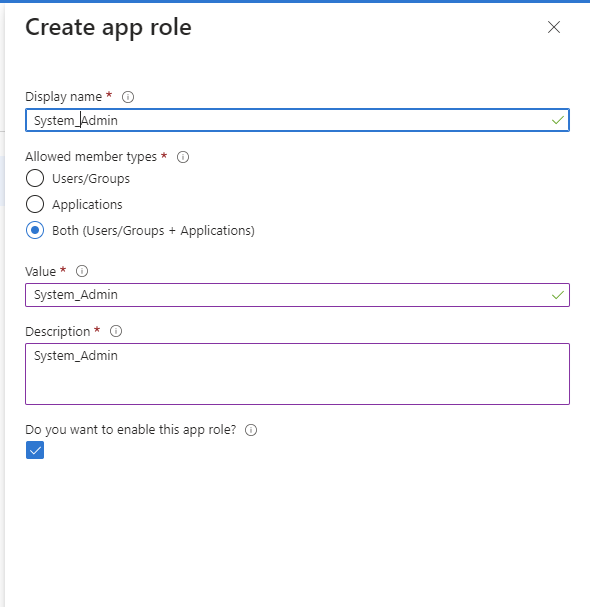
Provide the role details. The role value must be a valid UFM role. Otherwise, the login fails.
-
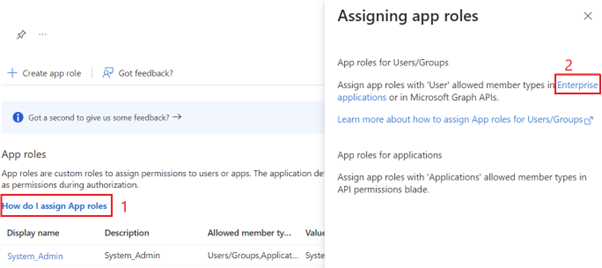
Assign the created role to the user. Follow these steps:
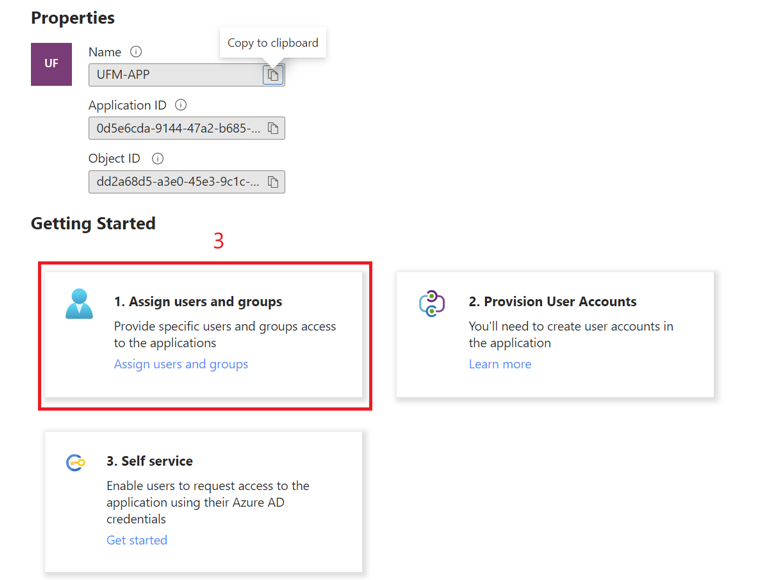
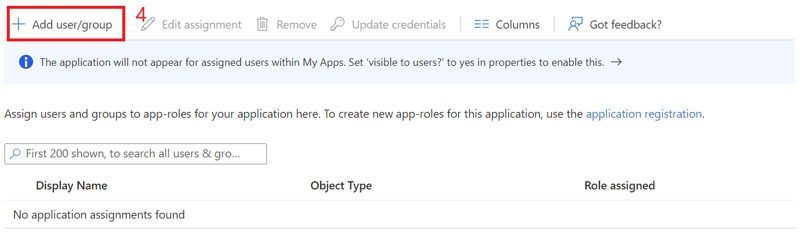
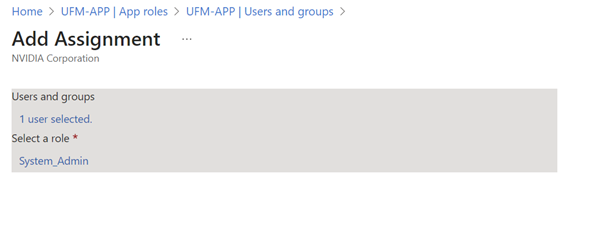
-
Click Overview in the side menu to view the application information, such as tenant ID, client ID, and other details.
Enable Azure Authentication From UFM
Azure authentication is disabled by default. To enable it, see Enabling Azure AD Authentication.
Azure Authentication Login Page
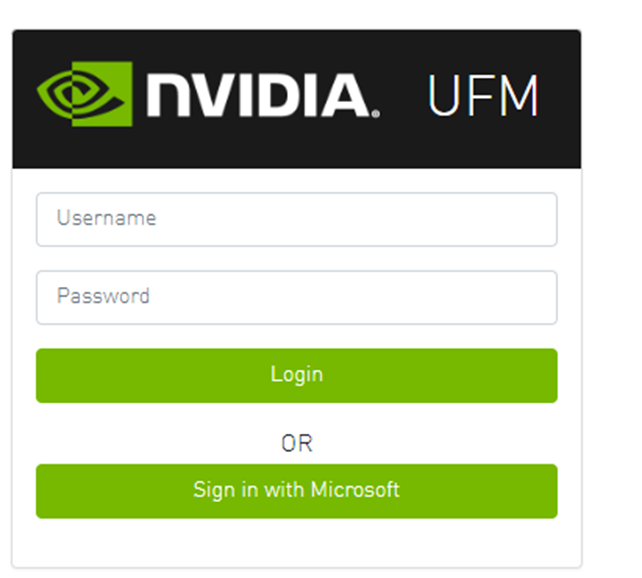
After you enable and configure Azure AD authentication, an additional button labeled Sign In with Microsoft appears on the primary UFM login page. The button leads to the main Microsoft sign-in page:
Kerberos Authentication
Kerberos is a network authentication protocol designed to provide strong authentication for client-server applications by using secret-key cryptography.
The Kerberos protocol works on the basis of tickets, which helps ensure that communication between various entities in a network is secure. It uses symmetric-key cryptography, which means both the client and servers share secret keys for encrypting and decrypting communication.
To enable Kerberos Authentication, see Enabling Kerberos Authentication.
Setting Up Kerberos Server Machine
To set up a system as a Kerberos server, perform the following:
-
Install the required packages:
#Redhat sudo yum install krb5-libs krb5-server # Ubuntu sudo apt-get install krb5-kdc krb5-admin-server -
Edit the Kerberos configuration file
/etc/krb5.confto reflect your realm, domain and other settings:[libdefaults] default_realm = YOUR-REALM [realms] YOUR-REALM = { kdc = your-kdc-server admin_server = your-admin-server } [domain_realm] your-domain = YOUR-REALM your-domain = YOUR-REALM
-
Use the
kdb5_utilcommand to create the Kerberos database:kdb5_util create -r YOUR-REALM -s -
Add administrative principals:
Kadmin.local addprinc -randkey HTTP/YOUR-HOST-NAME@YOUR-REALM -
Start KDC and Kadmin services:
sudo systemctl start krb5kdc kadmin sudo systemctl enable krb5kdc kadmin -
Generate a keytab file. The keytab file contains the secret key for a principal and is used to authenticate the service.
kadmin.local ktadd -k /path/to/your-keytab-file HTTP/YOUR-HOST-NAME@YOUR-REALMReplace
/path/to/your-keytab-filewith the actual path where you want to store the keytab file.
Setting Up Kerberos Client Machine
To set up a system as a Kerberos client, follow these steps:
-
Install the required packages. When you install UFM, the following packages are installed as dependencies:
#Redhat krb5-libs krb5-workstation mod_auth_gssapi # Ubuntu krb5-config krb5-user libapache2-mod-auth-gssapi -
Configure the
/etc/krb5.conffile to reflect your realm, domain, local names map and other settings:[libdefaults] default_realm = YOUR-REALM [realms] YOUR-REALM = { kdc = your-kdc-server admin_server = your-admin-server auth_to_local_names = { your-principle-name = your-local-user } } [domain_realm] your-domain = YOUR-REALM your-domain = YOUR-REALM -
Copy the keytab file from the Kerberos server to the machine where your service runs (the client). Keep the keytab file confidential.
Make sure that the keytab file exists and that Apache has read permission for it. Otherwise, Kerberos authentication does not function properly. -
Obtain a Kerberos ticket-granting ticket (TGT):
kinit -k -t /path/to/your-keytab-file HTTP/YOUR-HOST-NAME@YOUR-REALM -
Enable Kerberos Authentication from UFM. Kerberos authentication is disabled by default. To enable it, see Enabling Kerberos Authentication.
-
Test Kerberos authentication. You can use
curlto test whether the user can authenticate to UFM REST APIs using Kerberos.curl --negotiate -i -u : -k 'https://ufmc-eos01/ufmRestKrb/app/tokens'
Licensing
The UFM license is subscription-based and has the following subscription options:
-
1-year subscription
-
3-year subscription
-
5-year subscription
-
Evaluation 30-day trial license
UFM will continue to support old license types, but they are no longer available to obtain.
Two months before the expiration of your subscription license, UFM will warn you that your license will expire soon. After the subscription expires, UFM will continue to work with the expired license for two months beyond its expiration.
During this extra two-month period, UFM will generate a critical alarm indicating that the UFM license has expired and that you need to renew your subscription. Failing to do so within that 2-month period activates UFM Limited Mode. Limited mode blocks all REST APIs and access to the UFM web UI.
UFM enables functionality based on the license that was purchased and installed. This license determines the functionality and the maximum allowed number of nodes in the fabric.
To renew your UFM subscription, purchase a new license and install the new license file by downloading the license file to a temporary directory on the UFM master server and then copying the license file to the /opt/ufm/files/licenses/ directory.
UFM might not detect new license files if you download them directly to /opt/ufm/files/licenses. If UFM does not detect the new license file, you might need to restart UFM.
If several licenses are installed on the server (more than one license file exists under /opt/ufm/files/licenses/), UFM uses only the strongest license and takes into consideration the expiration date, and the managed device limits on it, regardless of any other licenses that may exist on the server.
Last updated: